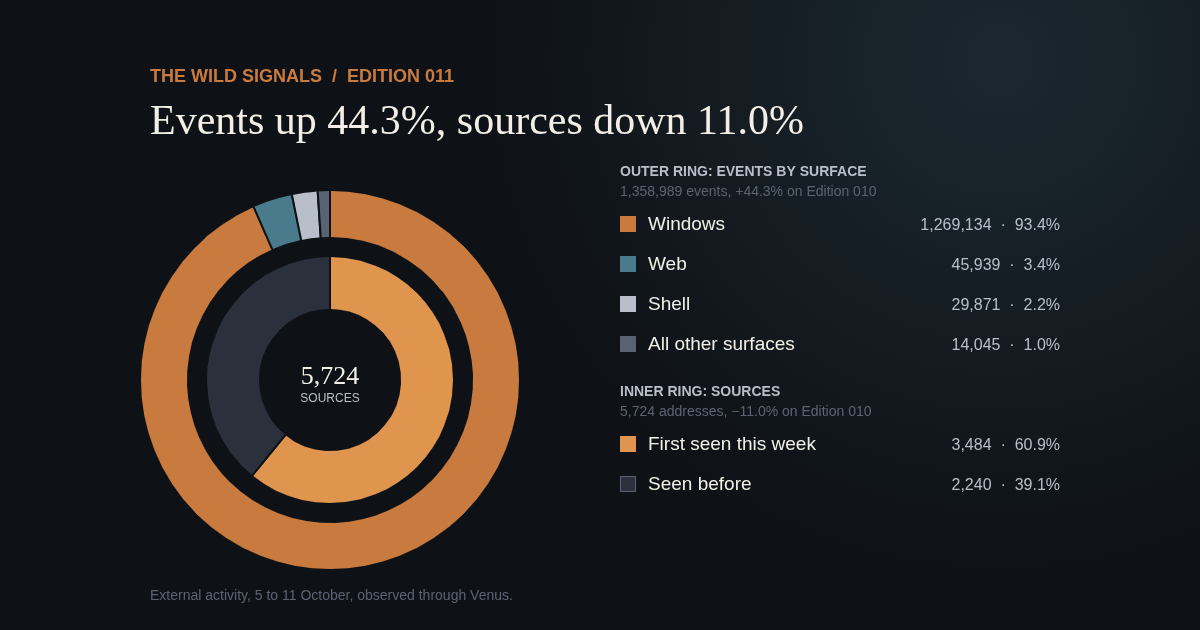

Events rose 44.3% while the number of sources fell 11.0%, and five older flaws joined the exploited list.
SECTION 01
What the signals mean
Events recorded on the Venus decoys rose 44.3% this week, to 1,358,989 from 941,813, while distinct sources fell 11.0%, to 5,724 from 6,431. The Windows surface supplied 412,933 of the 417,176 additional events. Campaigns, the groups of related sessions the decoys link together, rose to 3,429 from 980 in Edition 010.
Traversal doubled again from 28 sources
Directory traversal requests, which step outside a website’s public folder to read files behind it, rose 97.4%, to 1,741 from 882. All five of the most requested paths end at an environment file. The leader, /@fs/../.env, drew 81 requests against 39 and uses a route in the Vite development server. Four siblings under /assets../, /files../, /media../ and /static../ drew 45 each.
Consoles and script files grew
Requests for admin and management consoles rose 60.7%, to 3,766 from 2,344. The three most requested paths were /console, /admin and /dashboard, at 297, 286 and 284. Requests for server-side script files, the kind an attacker plants as a web shell, rose 32.5%, to 8,445 from 6,375, led by /index.php, /info.php and /phpinfo.php.
Secrets and archives fell again
Requests for secrets and configuration files fell 20.9%, to 16,335 from 20,645, and backup and archive requests fell 14.1%, to 589 from 686. /.env drew 630 requests against 643, /.env.local 263 against 375 and /.env.development 170 against 307. Terraform state, the record of every server and password a cloud build created, drew 63 requests for the root file against 67. /backup.zip fell to 17 from 67. Windows file sharing probes drew 182,365 events from 2,428 sources, down 2.6%.
Five older flaws joined the exploited catalogue
On 8 October five vulnerabilities were added to the catalogue of flaws confirmed as exploited in the wild, each with remediation due 11 October. Three date from 2015 and 2016: ProFTPD, Apache Struts and the BIND name server. The others are ONLYOFFICE Docs from 2021 and the Strapi content system from 2023. The ProFTPD flaw lets an attacker read and write files and has a public Metasploit module. Its EPSS score, a forecast of exploitation within 30 days, is 0.9950.
Forecasts rose on flaws already listed
Check Point’s remote access VPN flaw CVE-2026-50751, on the catalogue since June with ransomware use recorded, rose to 0.853 from 0.063. Zimbra rose to 0.717 from 0.117 and SharePoint to 0.695 from 0.175. A default-password flaw from 1998, CVE-1999-0502, stands at 0.5334 after one of its Metasploit login modules changed.
Exploitation reported before cataloguing
SonicWall SMA1000 was exploited three days after its patch, and Atlassian Data Center within hours of a public proof of concept. Rejetto HFS and AhsayCBS are also being exploited. None was on the catalogue by the end of the week.
The fingerprint cluster returned
The remote desktop tool identified by fingerprint 73ede1f461b6 ran from 262 addresses this week and produced 3,694 sessions, against 85 addresses and 2,352 sessions in Edition 010. It had stayed under a hundred addresses for two weeks.
What to act on
Patch the five catalogue additions first, since the 11 October deadline has passed. SonicWall, Atlassian and Citrix NetScaler follow. Remove site archives, Terraform state and every environment-file variant from any path a web server can reach, and keep development servers off external networks.
5 Oct – 11 Oct 2026
5 Oct – 11 Oct 2026
1,358,989 external events (+44.3%). 5,724 distinct sources (−11.0%). 13,896 sessions (−20.1%).
Against Edition 010’s published figures, events rose from 941,813 to 1,358,989, sources fell from 6,431 to 5,724 and sessions from 17,396 to 13,896. 3,484 sources were first observed this week and 2,240 had been seen before, against 3,891 and 2,540. By surface, Windows rose 48.2% to 1,269,134 from 856,201, Web rose 18.2% to 45,939 from 38,872, Shell fell 10.3% to 29,871 from 33,309 and Database fell 25.4% to 675 from 905. API rose 105.6% to 4,697 and Portal 106.8% to 4,708, while Auth fell 46.6% to 1,550 and VPN 52.3% to 2,415. Active campaigns rose to 3,429 from 980, up 249.9%, and 1,355 are flagged recurring, against 263.
Ranked signals
| Rank | Signal | Events | Ed. 010 | Change | Sources | Score |
|---|---|---|---|---|---|---|
| 1 | SQL Injection Probing | 2 | 12 | −83.3% | 1 | 0.4500 |
| 2 | Webshell / RCE Script Probing | 8,445 | 6,375 | +32.5% | 215 | 0.4352 |
| 3 | Sensitive File & Secret Exposure | 16,335 | 20,645 | −20.9% | 182 | 0.3903 |
| 4 | Directory / Path Traversal | 1,741 | 882 | +97.4% | 28 | 0.3843 |
| 5 | PHP Injection / Remote Include | 239 | 254 | −5.9% | 25 | 0.3643 |
| 6 | MySQL Credential Attack | 384 | 656 | −41.5% | 73 | 0.3551 |
| 7 | Admin Console Discovery | 3,766 | 2,344 | +60.7% | 130 | 0.3083 |
| 8 | Automated Scanner / Recon Tooling | 749 | 976 | −23.3% | 105 | 0.2761 |
| 9 | SSH Invalid-User Enumeration | 28,993 | 31,892 | −9.1%† | 458 | 0.2525 |
| 10 | SMB Credential Attack | 166,232 | 164,763 | +0.9% | 65 | 0.2342 |
| 11 | SSH Access Probing | 29,871 | 33,309 | −10.3%† | 858 | 0.1870 |
| 12 | SSH Campaign Targeting | 1,993 | 3,183 | −37.4%† | 249 | 0.1741 |
| 13 | SMB Access Probing | 182,365 | 187,206 | −2.6% | 2,428 | 0.1448 |
† The three SSH signals rest on the Shell feed, which ran at 98.21% batch coverage this period and complete in the comparison period. The change is computed against Edition 010’s published counts, and a small part of it may be collection.
Remote desktop fingerprint campaigns
| Client signature | Sessions | Ed. 010 | Change | Sources | Ed. 010 | Change |
|---|---|---|---|---|---|---|
TLS 73ede1f461b6 | 3,694 | 2,352 | +57.1% | 262 | 85 | +208.2% |
| RDP cookie “hello” | 576 | 416 | +38.5% | 121 | 115 | +5.2% |
| TLS 43e25370946f | 403 | 241 | +67.2% | 96 | 91 | +5.5% |
| RDP cookie “anonymous” | 364 | not published | – | 55 | not published | – |
Source counts cannot be added across the four signatures because one address may carry more than one. Only the first signature changed its footprint sharply. The other three grew by 5.2% to 5.5% in addresses and by far more in sessions.
Path families
| Family | Events | Ed. 010 | Change | Paths | Sources | Most requested |
|---|---|---|---|---|---|---|
| Sensitive File & Secret Exposure | 16,335 | 20,645 | −20.9% | 1,201 | 182 | /.env (630), /.env.local (263) |
| Backup & Archive Download Probing | 589 | 686 | −14.1% | 97 | 28 | /terraform.tfstate (63), /deploy/terraform.tfstate (20) |
| Webshell / RCE Script Probing | 8,445 | 6,375 | +32.5% | 2,030 | 215 | /index.php (161), /info.php (99) |
| Admin Console Discovery | 3,766 | 2,344 | +60.7% | 685 | 130 | /console (297), /admin (286) |
| Directory / Path Traversal | 1,741 | 882 | +97.4% | 78 | 28 | /@fs/../.env (81), /assets../.env (45) |
| SQL Injection Probing | 2 | 12 | −83.3% | 1 | 1 | /api/action/datastore_search_sql (2) |
Distinct paths rose to 685 from 308 in the admin family and to 2,030 from 1,441 in the webshell family, so those wordlists lengthened. The sensitive-file list shortened, to 1,201 paths from 1,507, and traversal paths fell to 78 from 90. The SQL injection requests came from a single source on 8 October and asked for one data-search path.
Representative paths
| Secrets and configuration | Events | Ed. 010 | Backup and archive | Events | Ed. 010 |
|---|---|---|---|---|---|
/.env | 630 | 643 | /terraform.tfstate | 63 | 67 |
/.env.local | 263 | 375 | /deploy/terraform.tfstate | 20 | not published |
/.git/config | 257 | 333 | /infra/terraform.tfstate | 20 | not published |
/.env.production | 212 | not published | /infrastructure/terraform.tfstate | 19 | not published |
/.env.development | 170 | 307 | /backup.zip | 17 | 67 |
Four of the five backup paths are Terraform state in different directories. /backup.tar.gz, /site.zip and /public_html.zip are no longer among the five most requested.
Behaviour progression
326 sessions carried behaviour from two or more distinct stages, against 343 in Edition 010.
| Ordering | Sessions | Ed. 010 | Change | Sources | Ed. 010 | Busiest source | Evasive |
|---|---|---|---|---|---|---|---|
| Discovery, then Exploitation | 229 | 239 | −4.2% | 134 | 144 | 21 (9.17%) | 3.49% |
| Exploitation, then Discovery | 97 | 104 | −6.7% | 73 | 97 | 8 (8.25%) | 18.56% |
The busiest source’s share of the forward ordering rose for a second week, to 9.17% from 8.79%, and the busiest source in the reverse ordering produced 8.25% of its sessions against 2.88%. A descending ordering is consistent with one tool issuing credential attempts before enumeration as much as with any escalation.
Vulnerability mapping
| Identifier | Description | Hits | Ed. 010 | Change | Sources | KEV |
|---|---|---|---|---|---|---|
| CWE-312 | Cleartext secrets (.env) | 13,345 | 15,448 | −13.6% | 97 | no |
| CVE-2021-41773 | Apache traversal | 8,485 | 6,414 | +32.3% | 219 | yes |
| CVE-2019-0232 | Tomcat CGI | 8,445 | 6,375 | +32.5% | 215 | no |
| CWE-527 | Exposed Git | 1,413 | 1,857 | −23.9% | 105 | no |
| CVE-2017-9841 | PHPUnit eval-stdin | 415 | 512 | −18.9% | 17 | yes |
| CVE-2012-1823 | PHP-CGI argument injection | 239 | 254 | −5.9% | 25 | yes |
14 of the mapping’s 17 identifiers were reached, against 13, and 6 of the 14 are on the KEV catalogue. CVE-2023-2982 rose to 140 hits from 82, CVE-2022-22963 fell to 49 from 100 and CVE-2022-22965 to 34 from 79, CVE-2021-42013 held at 40 against 39, and CVE-2017-12629 and CVE-2021-27905 each reached 20 against 10. CWE-22 appeared with 5 hits and CWE-89 fell to 2 from 12. Detection is inference from request path and behavioural tag, never observed exploitation.
Medulus correlation
17 vulnerabilities qualified this period, against 28 in Edition 010, with the actor and advisory association signal still withdrawn. Five entries were added to the CISA Known Exploited Vulnerabilities catalogue on 8 October, each due 11 October: ProFTPD CVE-2015-3306 (mod_copy file read and write, CVSS 10.0, EPSS 0.9950, Metasploit module), ONLYOFFICE Docs CVE-2021-3199 (traversal to code execution, EPSS up from 0.082 to 0.194), Apache Struts CVE-2016-3081 (dynamic method invocation, 0.9605), ISC BIND CVE-2015-5477 (TKEY denial of service, 0.9941) and Strapi CVE-2023-22894 (0.0361). Metasploit modules for the Langflow flaws CVE-2026-0769 (unauthenticated, EPSS 0.4169) and CVE-2026-7873 changed on 8 October, and CVE-2026-0768 rose from 0.085 to 0.232.
Reporting also describes exploitation of SonicWall SMA1000 CVE-2026-102255 (maximum severity, three days after its patch), Atlassian Data Center CVE-2026-21589, Rejetto HFS CVE-2026-61500 (session key recovery to administrator access and code execution) and two AhsayCBS flaws used to deploy web shells and XMRig miners. Citrix patched a further NetScaler flaw, CVE-2026-107406, that allows code execution or denial of service in SAML deployments, with an EPSS of 0.0047. None of these is on the catalogue.
Technical checks for the week
- Patch: ProFTPD, Apache Struts, ISC BIND, ONLYOFFICE Docs and Strapi. Remediation was due 11 October.
- Patch: SonicWall SMA1000, Atlassian Data Center and Citrix NetScaler for CVE-2026-107406.
- Remove: Terraform state, site archives, .git directories and every .env variant from web-reachable paths.
- Prioritise: Langflow, Check Point IKEv1 remote access and Rejetto HFS. Each has public exploit material or a rising forecast.
- Restrict: SMB to internal networks, and Vite development servers to local addresses.
- Review: default and blank passwords on database, FTP and SSH services.
Venus records activity reaching Elytra-operated decoy observation infrastructure. Medulus provides public vulnerability and threat-intelligence context. An observed request establishes an attempt, not a successful compromise. Week-on-week comparisons are drawn from the figures published in Edition 010.